

In the recent Anthropic-powered cyber attack report, “Autonomous” and “Vulnerability” were the two most standout terms. Anthropic’s call to action for the cybersecurity community to apply AI for defense in vulnerability assessment and remediation is a watershed moment.
In fact an entire phase of the attack path was dedicated to discovering and exploiting vulnerabilities:
“Phase 3: Vulnerability discovery and validation”
“the AI autonomously discovered vulnerabilities in targets selected by human operators and successfully exploited them in live operations”
“AI independently cataloging hundreds of discovered services and endpoints”
While this Anthropic attack was related to infrastructure endpoints i.e. server assets that were publicly accessible, it is a precursor to how AI can operationalize vulnerability detection and exploitation at scale for any type of endpoints, including employee devices.
As an industry, it’s a good time to pay attention to endpoint vulnerabilities tied to the workforce : employee devices. Device vulnerabilities were a “safe can of worms” that security & IT teams could afford to ignore or delay patching as they were not publicly accessible assets. But in today’s AI adversary landscape, we should assume that employees are going to get socially engineered through AI phishing attacks to click the wrong links, leaving those devices vulnerable to known exploits.
The “boring work” of patching known exploits and vulnerabilities on workforce laptops, desktops and devices becomes more important than ever - its what can harden and shield the organization from the next breach.
The last mile gap in vulnerability remediation for employee devices
Security and IT teams have always known and strived for basic endpoint security hygiene. But doing the basics is HARD. The last mile of work in endpoint vulnerability patching is messy, time-consuming and manual.
This manual process outlined in the image is how and where it all breaks down. First it requires a ton of manual work to map and track vulnerabilities tied to employee devices and applications, and then engaging them for the remediation process is riddled with toil. This means tracking in spreadsheets, sending email reminders, escalating via emails and messages, then reporting it to managers and the end result is that the vulnerability backlog keeps piling up and compounds workforce risk with each patch delay that lives with the employee and their devices. It’s why we see customers show us their EDR and VM tool dashboards with out-of-SLA vulnerabilities in four and five digits.
AI agents that engage employees at scale for personalized remediation
Amplifier’s human risk graph powers a live system of record for each employee’s risk — that solves the mapping problem of user identity, device OS and application vulnerabilities, device posture and endpoint tooling coverage gaps. The graph serves as important data and context required for meaningful user engagements through agentic AI automation.
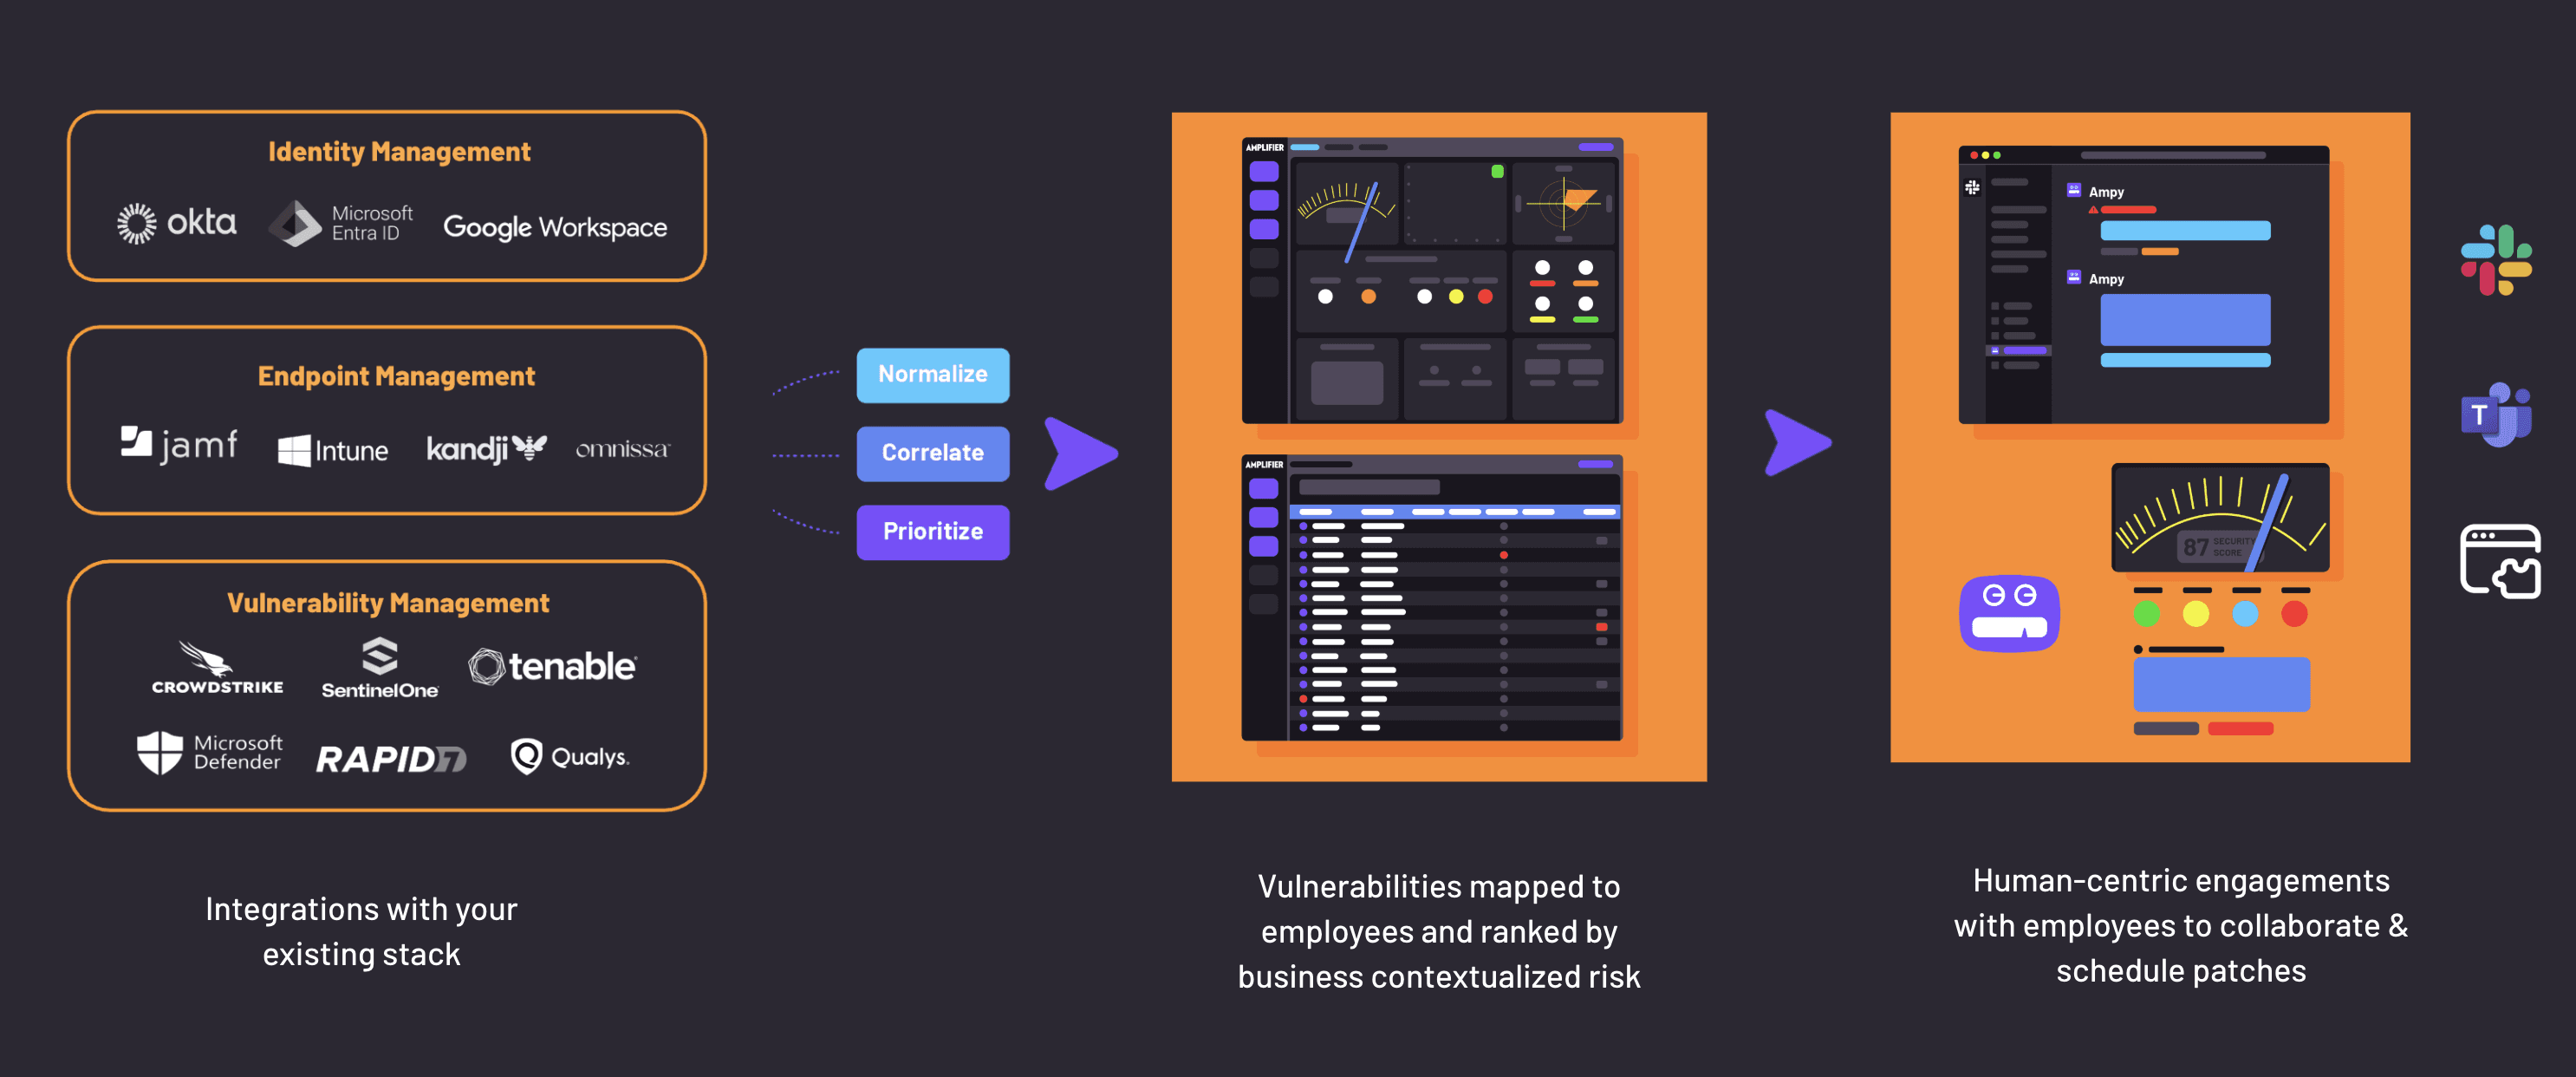
Amplifier’s AI agents liberate IT and Security teams from vulnerability remediation follow-ups so they can focus on impact. AI agents engage users for taking remediation actions through easy calendar scheduling – invoking existing patch automation tools or just using AI generated instructions to fix issues.
Amplifier turns vulnerability alerts into employee-driven remediation by guiding employees through patches and updates during their natural flow of work, closing security gaps in hours instead of months — all without disrupting workforce productivity or employee experience.
This interactive demo shows how Ampy, the AI security engineer, helps employees close CrowdStrike vulnerabilities on their devices through friendly, one-on-one guidance with clear patch actions and step-by-step instructions.
It rapidly solves the problem of critical security patches sitting in deployment queues for months while IT teams struggle to coordinate updates across thousands of endpoints.
Time to fix the “assumed vulnerability risk” backlog
One thing is clear that current defensive approaches are no longer sustainable with this new AI adversary landscape. Endpoint vulnerabilities are a ticking time bomb waiting to explode when AI attackers exploit known vulnerabilities from the pile of “assumed risk” debt.
Vulnerability management is one of the most basic preventative measures, but traditionally one of the hardest to enforce. It’s constant ping-pong between different teams – GRC, Vuln Management, App Security, Enterprise Security, Corporate Security, IT and the workforce always chasing down process gaps and delays.
We’ve seen a lot of positive evidence that non-threatening, personalized and engaging outreach to employees does move the needle - way more than decades of traditional approaches of escalating and scolding has.
Anthropic has described only the first known case, but security teams are now acknowledging they cannot operate this way of “compartmentalizing risk” anymore. The AI adversary landscape has changed it for them, because they know in today’s world this is not an “if” but “when”.
It’s why security teams now nod their heads that this “last mile of work” really matters. Now it’s time for this last mile to be fixed, but this time it’s important. And this time, there is a real solution – where AI can empower employees to quickly turn awareness into action.
Frequently Asked Questions
What is the “last mile gap” in endpoint vulnerability remediation?
The last mile gap is the manual, time-consuming work of getting employees to actually apply a patch after a vulnerability is found. Security and IT teams can detect issues quickly with EDR and vulnerability management tools, but driving the fix through spreadsheets, email reminders, and escalations is where remediation stalls and backlogs build.
Why are employee device vulnerabilities a bigger risk now than in the past?
Employee devices were historically deprioritized because, unlike server infrastructure, they weren’t publicly accessible. That assumption no longer holds. AI-powered phishing can trick employees into exposing their devices, and Anthropic’s disclosed cyberattack showed AI can autonomously discover and exploit vulnerabilities at scale, making unpatched employee devices a realistic attack path.
What did Anthropic’s cyberattack report find about AI and vulnerability exploitation?
Anthropic disclosed an attack in which AI autonomously discovered, validated, and exploited vulnerabilities across hundreds of cataloged services and endpoints with minimal human direction. That case involved infrastructure endpoints, but it signals that AI can operationalize vulnerability discovery and exploitation against any endpoint, including employee laptops and desktops.
Why has vulnerability management for employee devices been so hard to enforce?
It requires coordination across multiple teams — GRC, vulnerability management, application security, corporate security, IT, and employees themselves — each handing the problem to the next. Without a system connecting detection to remediation, vulnerabilities pile up in spreadsheets and email threads instead of getting fixed, and SLA breaches climb into the thousands.
How does Amplifier’s human risk graph help close endpoint vulnerabilities?
Amplifier’s human risk graph maps each employee to their identity, device operating system, application vulnerabilities, device posture, and security tooling coverage in one live system of record. That unified mapping gives AI agents the context to engage the right employee, on the right device, with the right fix.
How do Amplifier’s AI agents get employees to actually remediate vulnerabilities?
Amplifier’s AI agents reach employees directly through calendar scheduling, existing patch automation tools, or step-by-step AI-generated instructions, and guide them through the fix during their normal workflow. This replaces manual follow-ups from IT and security teams with personalized, self-service remediation that doesn’t disrupt productivity.
What results can organizations expect from AI-driven employee engagement on patching?
Organizations using this approach can close vulnerability gaps in hours instead of months, according to Amplifier. The company’s interactive demo shows its AI security engineer, Ampy, guiding employees through closing CrowdStrike vulnerabilities with direct, one-on-one instructions rather than ticket queues or escalation emails.
Why does personalized outreach work better than traditional escalation for patching?
Traditional approaches rely on escalating, chasing, and reporting delinquent patches to managers — an approach security teams describe as “scolding” that rarely changes behavior. Non-threatening, personalized outreach that explains what’s wrong and walks employees through the fix has proven far more effective at driving real remediation.
Latest Blogs
Related Blogs & News


Watch